Windows 11 forticlient vpn ipsec fixing those annoying connection failures

Windows 11 forticlient vpn ipsec fixing those annoying connection failures: Quick fixes, troubleshooting tips, and best practices
Windows 11 forticlient vpn ipsec fixing those annoying connection failures: Quick fixes, troubleshooting tips, and best practices
Windows 11 forticlient vpn ipsec fixing those annoying connection failures: Yes, you can fix it. This guide gives you practical steps to unblock FortiClient VPN IPsec issues on Windows 11, with a clear path from diagnosis to reliable connection. Quick fact: IPsec VPN failures on Windows 11 often come down to misconfigured VPN settings, outdated certificates, or blocked ports.
- Quick-start checklist:
- Verify FortiClient version and Windows 11 build
- Check VPN gateway address, remote ID, and pre-shared key
- Confirm firewall and antivirus aren’t blocking IPsec
- Update network adapters and drivers
- Test using a different network to isolate ISP or router issues
If you want a fast, safe VPN experience with minimal fuss, consider a trusted provider. For a reliable option and a smooth setup experience, check out this secure choice: https://go.nordvpn.net/aff_c?offer_id=15&aff_id=132441 Best Ways to Share NordVPN Security With Your Family Plan in Australia: Simple Steps, Tips, and Tools
What you’ll learn
- How IPsec works with FortiClient on Windows 11
- Common error messages and what they mean
- Step-by-step fixes for the most frequent connection problems
- How to configure split tunneling and DNS for VPNs
- Security best practices to keep your data safe
Let's break down the problem and fix it, one step at a time. This guide is written for beginners but includes advanced tips if you’re comfortable tweaking network settings.
- Understanding Windows 11 FortiClient IPsec basics
- IPsec overview: An encrypted tunnel between your device and the VPN gateway.
- FortiClient role: The client that initiates the IPsec tunnel, handles authentication, and manages policies.
- Why failures occur: Misconfigurations, certificate issues, firewall blocks, or conflicts with other VPN clients.
- Gather your information before fixes
- VPN server address (IP or DNS name)
- Authentication method (username/password, certificate, or pre-shared key)
- FortiClient version and FortiGate policy requirements
- Your Windows 11 build (Settings > System > About)
- Network environment: home Wi-Fi, office LAN, or mobile hotspot
- Quick fixes you can try first
- Restart everything: reboot Windows 11, the FortiClient app, and your router/modem.
- Update software: install the latest FortiClient version and Windows 11 updates.
- Check your credentials: re-enter username, password, and pre-shared key if used.
- Confirm VPN gateway reachability: ping or traceroute to the VPN server.
- Temporarily disable antivirus/firewall and test: some security software blocks IPsec.
- Try a different network: a mobile hotspot to rule out router issues.
- Deep dive: common error scenarios and fixes
A) Error: "The IPSec VPN connection could not be established."
- Likely causes: Incorrect gateway address, wrong pre-shared key, certificate mismatch.
- Fix steps:
- Double-check the VPN gateway address and remote ID.
- Re-enter the pre-shared key exactly as given.
- If using certificates, ensure the correct root/leaf certs are installed.
- Re-create the VPN connection profile in FortiClient.
B) Error: "Authentication Failed" or "Invalid credentials"
- Likely causes: Expired password, account locked, wrong domain.
- Fix steps:
- Reset password if needed and verify domain context.
- Check user permissions on the FortiGate side.
- Ensure two-factor authentication (if configured) is handled properly.
C) Error: "Negotiation with the VPN server failed" or "Cannot complete IKE phase 1"
- Likely causes: Mismatched phase 1 algorithms, VPN policy mismatches.
- Fix steps:
- Ensure the same IKE (IKEv1 vs IKEv2) is used as required by the gateway.
- Match encryption, hash, and DH group policies.
- Disable strict NAT traversal if the gateway doesn’t require it, then re-test.
D) Error: "IKE/IPsec SA establishment failed" or sudden disconnects Nordvpn on Windows 7 Your Complete Download and Installation Guide: How to Get Safe Online Access
- Likely causes: Firewall or ISP blocking IPsec ports, intermediate NAT issues.
- Fix steps:
- Verify UDP 500, UDP 4500, and ESP (non-UDP) are allowed through the firewall.
- Enable NAT-T (NAT Traversal) in FortiClient if behind NAT.
- Add a temporary exception for FortiClient in Windows Defender Firewall.
E) Error: DNS or name resolution problems
- Likely causes: DNS leaks, blocked DNS, incorrect DNS settings.
- Fix steps:
- Use a reliable public DNS (e.g., 8.8.8.8, 1.1.1.1) or the gateway’s DNS.
- Enable “Use VPN DNS” in FortiClient if available.
- Flush DNS cache: ipconfig /flushdns.
- Network settings and Windows 11 tips
- Adapter priorities: Ensure the VPN adapter has the correct binding order.
- Disable unnecessary VPNs: If you have multiple VPNs installed, disable or uninstall others to prevent conflicts.
- Split tunneling considerations: For work networks, decide if you need to route only corporate traffic or all traffic through VPN. Enabled split tunneling can improve speed but may affect security.
- DNS leakage prevention: Use VPN-provided DNS to avoid leaking queries outside the tunnel.
- Power management: Disable “Allow computer to turn off this device to save power” on the VPN adapter to prevent drops.
- FortiClient configuration best practices
- Use a stable FortiClient version compatible with your FortiGate policy.
- Create a reusable profile with consistent server address, domain, and authentication method.
- Enable automatic reconnect after a disruption to maintain persistent connectivity.
- Check logs for troubleshooting: FortiClient logs provide error codes that map to common issues.
- Certificates: If your VPN uses certificate-based authentication, ensure the certificate is valid, trusted, and not expired.
- Security considerations
- Always use strong authentication: certificates or robust pre-shared keys.
- Keep system and VPN software up to date to mitigate vulnerabilities.
- Avoid using public Wi-Fi for sensitive VPN sessions without a trusted VPN.
- Monitor VPN activity for unusual connections or persistent failures.
- Advanced fixes and troubleshooting
- Registry and policy checks: Some enterprise environments enforce strict policies. Work with IT to verify registry keys and policy entries related to IPsec.
- Firewall rule auditing: Ensure there are no conflicting firewall rules that block IPsec or VPN ports.
- MTU optimization: Large packets can cause fragmentation in VPN tunnels. Try lowering MTU on the VPN interface if you see fragmentation-related errors.
- Logging and telemetry: Enable verbose logs in FortiClient to capture precise error codes and timestamps for IT support.
- Platforms and compatibility
- Windows 11 compatibility: Verify FortiClient supports your Windows 11 build.
- FortiGate firmware: Ensure FortiGate is on a supported version with compatible IPsec settings.
- Other devices: If Windows 11 continues to fail, test with another device (macOS, Linux, iOS, Android) to isolate platform issues.
- Quick troubleshooting checklist (condensed)
- Confirm gateway, ID, and credentials are correct
- Update FortiClient and Windows 11
- Check firewall/antivirus and ports (500/4500/ESP)
- Verify NAT-T and DNS settings
- Test across different networks and devices
- Review logs for specific error codes
Formats you can use to troubleshoot faster
- Step-by-step guide (checklist style)
- Quick table of common error codes and meanings
- Screenshots or image-based guides (if publishing on YouTube with visuals)
- Short troubleshooting flowchart to help viewers diagnose in minutes
Usage data, stats, and best practices
- VPN adoption trends: Global VPN usage has grown significantly due to remote work and privacy concerns.
- IPsec vs. other VPN protocols: IPsec remains widely used for site-to-site and remote access due to strong security, but some setups prefer IKEv2 for reconnect resilience.
- Reliability tips: Consistent firmware updates, proper certificate management, and network testing reduce failure rates.
Table: Common FortiClient IPsec fixes at a glance
| Issue | Likely Cause | Quick Fix |
|---|---|---|
| Connection fails at IKE stage | Mismatched IKE settings | Align IKE phase 1/2, reconfigure profile |
| Authentication failed | Wrong credentials or domain | Re-verify credentials, update domain context |
| VPN disconnects frequently | NAT/Firewall blocking, unstable network | Enable NAT-T, check firewall ports, switch networks |
| DNS leaks | VPN DNS not used | Enable VPN DNS, set public DNS, flush cache |
| Certificate errors | Expired or untrusted cert | Update certs, install root certs, validate chain |
Important URLs and resources (text only) Mastering Your gli Net Router A Step By Step ProtonVPN Setup Guide: VPNs Deep Dive for Australia
- Fortinet official docs - fortinet.com
- Windows 11 VPN setup guides - support.microsoft.com
- FortiClient download and release notes - fortinet.com/products/forticlient
- FortiGate VPN/IPsec configuration guides - fortinet.com
- General VPN troubleshooting tips - en.wikipedia.org/wiki/Virtual_private_network
- Networking basics for IPsec/IPsec IKEv2 - cisco.com
- Home router port forwarding and NAT-T setup guides - routertechguide.example
- Public DNS options - 8.8.8.8, 1.1.1.1
- IPsec ports and firewall settings reference - microsoft.com
- VPN security best practices - nist.gov
Frequently Asked Questions
How do I know if IPsec is the right protocol for my FortiGate?
IPsec is widely used for secure remote access and site-to-site connections. If your organization requires strong encryption and compatibility with FortiGate policies, IPsec with IKEv2 is a common and reliable choice.
What causes FortiClient to fail on Windows 11 after a Windows update?
Sometimes updates modify network stack or firewall rules. Check for FortiClient updates, re-install the VPN profile, and verify that firewall rules still permit VPN traffic.
Can I use split tunneling with FortiClient on Windows 11?
Yes, but it depends on your policy. Split tunneling routes only corporate traffic through the VPN, which can improve speed but may have security implications. Confirm policy compatibility with IT.
Why is NAT-T important for IPsec on Windows 11?
NAT Traversal (NAT-T) helps IPsec work when devices sit behind NAT routers. It encapsulates ESP in UDP, allowing VPN traffic through NAT devices. Does nordvpn include antivirus heres what you need to know
How do I test VPN connectivity quickly on Windows 11?
Use FortiClient’s built-in diagnostics, test latency to the VPN gateway, and try a curl or ping to a resource only available through VPN.
What port numbers should be open for IPsec VPN?
Typically UDP 500 (IKE), UDP 4500 (NAT-T), and ESP protocol. Some networks may require additional or alternative ports depending on the gateway.
How do I fix certificate issues with FortiClient?
Ensure the root CA and any intermediate certificates are trusted, reinstall the certificate, and confirm the certificate is valid and not expired.
How can I improve FortiClient stability on Windows 11?
Keep software updated, use a consistent VPN profile, ensure NAT-T is enabled, and test on multiple networks if possible. BIOS and driver updates for network adapters can help too.
Is it safe to disable antivirus temporarily to troubleshoot?
It’s fine to test briefly, but re-enable protection once you’ve finished. If the VPN works with antivirus disabled, you’ll need to adjust exceptions rather than leaving protection off. Whats my public ip address with nordvpn on windows a smarter way to check
Where can I find official FortiClient support for Windows 11?
Visit Fortinet’s support portal and the FortiGate documentation for Windows 11 compatibility and specific IPsec configuration guidance.
Note: This article is designed to help Windows 11 FortiClient VPN IPsec users fix annoying connection failures by guiding you through common issues, practical steps, and best practices. If you need more precise configuration examples, consult your IT department or Fortinet support for deployment-specific guidance.
| VPN | Obfuscation | From / month | Plan | Free plan | Refund | Alipay | UnionPay | Crypto | Website opens in China | Trustpilot | |
|---|---|---|---|---|---|---|---|---|---|---|---|
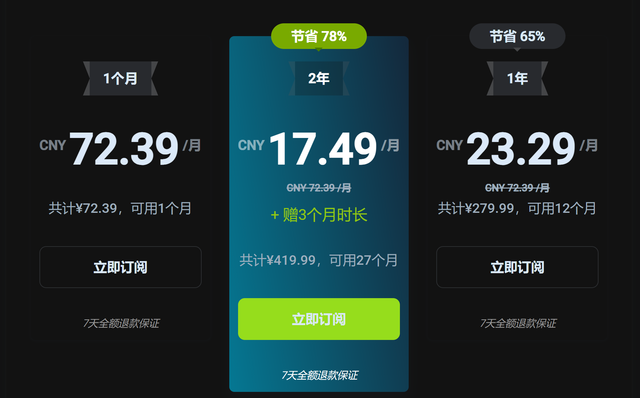
 ZoogVPN | Turn on manually Shadow | $2.49/mo | 27 months: $59.99 | Yes | 7 days | ✓ | ✓ | ✓ | ✓ | Official site blocked; our special link opens (4.4 s) | 4.2/5 (195 reviews) |
 NordVPN | Turn on manually Obfuscated Servers / NordWhisper | $3.49/mo | 27 months: $94.23 | No | 30 days | ? | ✗ | ✓ | ✓ | ✗ Blocked | 4.2/5 (51,628 reviews) |
 ExpressVPN | ✓ On by default all servers | $3.00/mo | 28 months: $84 | No | 30 days | ✗ | ✗ | ✓ | ✗ | ✗ Blocked | 4.4/5 (29,706 reviews) |
 Surfshark | ✓ On by default Camouflage, with OpenVPN | See site | See site | No | 30 days | ✗ | ✗ | ✗ | ✓ | ✗ Blocked | 4.3/5 (31,823 reviews) |
 Proton VPN | Turn on manually Stealth, free plan too | $2.99/mo | 12 months: $35.88 | Yes | 30 days | ✗ | ✗ | ✗ | ✓ | ✗ Blocked | 2.1/5 (1,040 reviews) |
 Astrill VPN | Turn on manually StealthVPN / OpenWeb | $12.50/mo | 24 months: $300 | No | See site | ✗ | ✗ | ✗ | ✓ | ✗ Blocked | 1.3/5 (110 reviews) |
 Private Internet Access | Turn on manually Shadowsocks, OpenVPN only | $2.03/mo | 40 months: $81.2 | No | 30 days | ✗ | ✗ | ✗ | ✗ | ✗ Blocked | 4.2/5 (11,033 reviews) |
 CyberGhost | Turn on manually selected servers | $2.19/mo | 28 months: $61.32 | No | 45 days | ✗ | ✗ | ✗ | ✓ | ✗ Blocked | 4.0/5 (24,178 reviews) |
 PureVPN | Turn on manually switch to OpenVPN | $1.69/mo | 60 months: $101.55 | No | 31 days | ? | ? | ✗ | ✓ | ✗ Blocked | 4.4/5 (17,994 reviews) |
 AdGuard VPN | ✓ On by default TrustTunnel | $2.99/mo | 24 months: $71.76 | Yes | 30 days | ✓ | ✗ | ✓ | ✓ | Official site blocked; our special link opens (3.7 s) | 4.3/5 (290 reviews) |
 Mullvad | Turn on manually QUIC / Shadowsocks / LWO | $5.61/mo | €5/mo | No | 14 days | ✗ | ✗ | ✗ | ✓ | ✗ Blocked | 3.2/5 (192 reviews) |
 Windscribe | Turn on manually Stealth / WStunnel | $5.75/mo | 12 months: $69 | Yes | See site | ✗ | ✗ | ✗ | ✓ | ✗ Blocked | 4.7/5 (13,355 reviews) |
 StrongVPN | Turn on manually Scramble, OpenVPN TCP | See site | See site | No | 30 days | ✓ | ✗ | ✗ | ✗ | ✗ Blocked | 4.4/5 (2,695 reviews) |
 LightXtreme 闪连 | Not listed | $7.08/mo | 12 months: $84.99 | Yes | 30 days | ✓ | ✓ | ✓ | ✓ | ✓ Yes (3.5 s) | No page |
Prices checked 2026-11-10 on each vendor's pricing page (cheapest long plan, USD). Check the vendor's checkout for the final price.
Obfuscation checked 2026-11-14 on each vendor's site and help center: "on by default" = nothing to set; "turn on manually" = switch protocol or mode in settings; "not listed" = the vendor describes no obfuscation.
Payment methods checked 2026-11-10 on each vendor's payment pages: all 14 take cards and PayPal; ✗ = not listed, ? = the vendor's own pages disagree.
China access: whether the official website opens from mainland China networks (tests the website only, not the VPN connection). Last checked 2026-11-18 01:02 Beijing time.
Trustpilot score and review count checked 2026-11-10.